In this article, we will discuss the importance of mobile app security for every business, common security threats, and practical ways to protect applications from cyberattacks. We will also explore how securing mobile apps helps businesses protect sensitive information, build customer trust, and maintain a strong reputation. Whether you are developing a new application or improving an existing one, prioritizing mobile app data security is essential for providing users with a safe and reliable experience.
What exactly is “Mobile App Security?”
Mobile app security, as the name says, is the process of protecting mobile applications from external dangers such as cybercriminals, computer viruses, and other forms of online danger. These infections and other cyber dangers might put sensitive data, such as financial information, at risk from hackers.
Effective security for mobile applications involves protecting application code, user credentials, personal information, financial records, APIs, and backend servers from unauthorized access. Businesses should adopt a comprehensive approach that includes encryption, secure authentication, regular security testing, and continuous monitoring. Investing in reliable mobile application security services can help identify vulnerabilities early and reduce the risk of data breaches.
Threats to the Security of Mobile Applications
Understanding common mobile security threats is the first step toward securing mobile apps. From insecure data storage and weak authentication to reverse engineering and server-side vulnerabilities, these risks can expose sensitive business and customer information. Identifying these weaknesses early helps businesses strengthen their applications and maintain better mobile app data security.
1. Lack of Binary Protection
Suppose your mobile application does not have binary protection. In that case, it will be simple for a hacker to examine, reverse-engineer, or modify the code in order to introduce malware and carry out some strange features. Theft of confidential data and intellectual property, loss of revenue and privacy, illegal access, fraud, and damage to the reputation of a brand can all result from a lack of binary protection.
2. Theft of Financial Records
Hackers have the ability to make transactions after stealing the user’s financial data, such as credit card or debit card information. Hackers employ numerous viruses, such as trojans, to trick Android users into getting their financial details, such as credit card information.
Cybercriminals usually infect your mobile devices with malware and collect vital financial information from their devices. Hackers are able to obtain the user’s financial information and conduct fraudulent transactions using the user’s card using these methods.
3. Theft of Vital Information
Hackers can compromise a wide variety of other crucial data in addition to financial information, such as the account credentials of any user or any website. Downloaded applications are a common vector for the spread of malware of a similar variety.
Malware has the ability to infect the device, coerce it into sending or receiving messages, and request authorization to access the location of the device. Additionally, it has the capability to read the contact list and support push alerts and engage in any activity that could be hazardous without your authorization.
4. Unintentional Data Leakage
Bugs in the operating system, carelessness on the part of the user, or an accidental mistake on the part of the developer might all lead to the sensitive information of your app being kept in insecure locations on the user’s smartphone. Upon having access to this data, hackers can easily steal your personal information.
5. Insufficiently Secure Authorization and Authentication
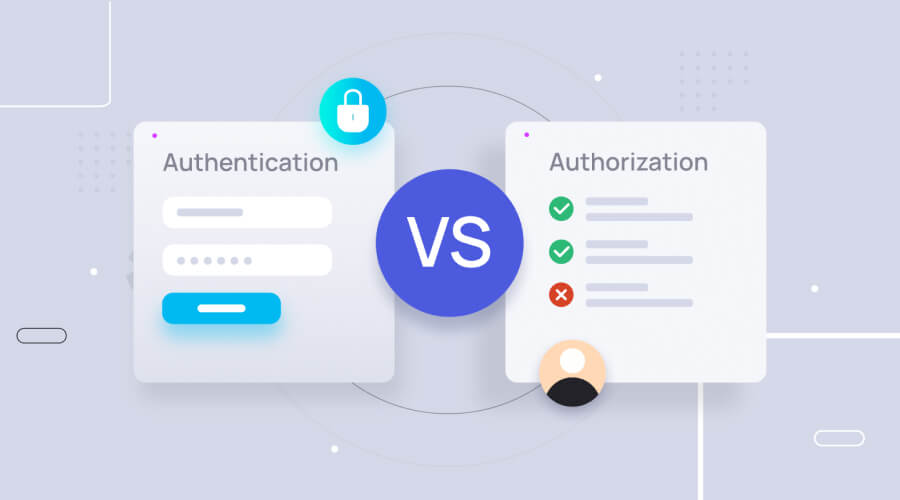
More often than not, poor authentication or authorization inputs lead to online crimes. In most cases, this issue arises because the mobile application in question has a weak password policy, which ultimately results in insecure authentication.
6. The Incorrect Storage of Data
This is another one of the most significant dangers to mobile app users. This vulnerability can be easily exploited if the mobile app saves sensitive data such as passwords, PINs, or any other personal or financial information without using encryption. If the hackers manage to get their hands on this information.
7. Weak Server-Side Controls
The mobile developers don’t pay nearly enough attention to the safety of the mobile app servers. Therefore, when communication takes place between users and mobile apps, the system is put in a vulnerable state and is subject to potential security threats.
More often than not, it happens when you hire a random or less skilled app development company to do the job. A professional mobile app development company, such as WeeTech that has a team of expert and skilled developers who use their experience and expertise to create safe and secure mobile apps.
8. Revenue loss
Hackers have the ability to gain unauthorized access to the premium edition of the software or its additional features. This could result in a drop in total revenue. This kind of hacking is most commonly carried out in gaming and utility applications.
How To Develop Secure Apps?
Businesses can improve application protection by following established security practices throughout the development lifecycle. A reliable mobile security app strategy should include secure coding, data encryption, authentication controls, API protection, and regular vulnerability assessments. These practices help developers address potential risks before applications reach end users.
1. Exercise Caution
Developers should exercise caution while making an app and incorporate features to help them find and fix security flaws. Developers should check that their programs can’t be modified or reverse-engineered in any way.
To protect your application from these kinds of attacks, encrypting the source code is a good idea.
2. Conduct a Complete Quality Assurance and Security Audit
Before releasing an application, the developer must conduct a complete quality assurance and security audit. In particular, penetration testing can help you protect your mobile apps from potential security flaws. Identifying security flaws is crucial as these openings can potentially develop into dangers that grant access to mobile data and functionalities.
3. Protect Information While in Transit
When it comes to preventing unauthorized parties from accessing or stealing sensitive data as it travels from client to server, Secure Sockets Layer (SSL) or Virtual Private Network (VPN) comes in handy. SSL and VPNs are great tunnels to encrypt and secure user data.
4. Implement Cutting-edge Cryptographic Methods
Implementing up-to-date encryption techniques, such as AES with 512-bit encryption, 256-bit encryption, and SHA-256, is crucial. Also, you should conduct manual penetration testing along with threat modeling on your applications before releasing them to the public.
5. Robust Authentication
Security flaws occur due to a lack of strong authentication. The apps should be built so that only complex alphanumeric passwords are accepted.
Biometric authentication, such as a fingerprint or retina scan, can be used to fortify the safety of particularly sensitive apps.
The vast majority of mobile apps use client-server architecture. It’s crucial to install safety features to protect backend servers against intrusion by malicious users.
Most programmers believe that APIs are restricted to only the apps that have been specifically designed to use them. API authentication and transport protocols can vary from one mobile platform to the next, so it’s important to make sure your APIs work with the one you’re targeting.
Why Is Mobile Application Security Important For A Business?
Strong mobile app data security is important for protecting customer privacy, preventing financial losses, and maintaining compliance with applicable data protection requirements. A single security incident can damage customer trust and affect business operations. By investing in proactive security measures and professional mobile application security services, businesses can reduce vulnerabilities and provide customers with a more secure digital experience.
Although businesses are aware of the significance of data center security in general, relatively few have well-defined application security policies in place. This makes it difficult for businesses to keep up with, let alone get ahead of, cybercriminals.
Identifying and closing security holes is, in fact, the most important part of the application security process. However, as cybercriminals create increasingly complex methods, businesses need to keep one step ahead of them, and ideally several steps ahead, using contemporary security technologies.
There is simply no space for ineffective security strategies in this day and age due to the fact that threats are becoming harder to detect and even more damaging to a company.
Not having the right means in place to prevent security breaches from occurring can soil your business’ name. A secure app can help you have increased revenues and better clientele.
Due to the ever-increasing danger of harmful actions, developers must give top emphasis to mobile app security issues. As a result, people are more hesitant to download programs they don’t know are safe.
The majority of people employed in the world do their jobs from home these days, and some businesses hire independent contractors who use their own personal laptops or desktop computers to complete their assignments for those businesses. This method exposes businesses to the possibility of cyberattacks. A single vulnerability is all that is needed to compromise the customers’ and company’s systems’ respective levels of privacy. As a result, it is vital for developers to inspect the app’s security; developers are required to provide the most up-to-date security features to protect user privacy and data.
If mobile app security is implemented correctly, it gives users the ability to safeguard sensitive and private data, protect themselves against data loss, malware, and virus assaults, and defend themselves against legal action brought on by unprotected systems.
Best Practices for Securing Mobile Apps
Securing mobile apps requires a proactive approach that considers security at every stage of the application development lifecycle. Businesses should not wait until a security breach occurs to address vulnerabilities. Instead, they should integrate security measures into planning, development, testing, deployment, and maintenance.
Here are some essential practices to strengthen mobile application security:
Encrypt sensitive information: Protect personal details, payment information, and login credentials both in transit and at rest.
Use secure authentication: Implement multi-factor authentication, biometric verification where appropriate, and secure session management.
Protect APIs and backend systems: Apply access controls, authorization checks, rate limiting, and secure communication protocols.
Conduct regular security testing: Perform vulnerability assessments, code reviews, and penetration testing to identify weaknesses.
Keep applications updated: Fix known vulnerabilities by updating application dependencies, libraries, and security components.
Follow data minimization principles: Collect and retain only the information necessary for the application’s intended functionality.
Businesses looking for professional mobile application security services can work with experienced development teams to assess vulnerabilities, strengthen application architecture, and implement appropriate security controls. A well-planned approach to security for mobile applications helps protect customer information, reduce business risks, and build user confidence.
Wrapping it up…
Mobile application security is essential for businesses that want to protect customer information, prevent cyberattacks, and build lasting trust. From secure authentication and encryption to regular security testing, every measure contributes to securing mobile apps against evolving threats.
Businesses should prioritize security for mobile applications throughout the development lifecycle rather than treating it as a final step before launch. A comprehensive approach to mobile app data security helps minimize risks and supports a safer user experience.
WeeTech follows a rigorous security testing approach and applies mobile app development best practices to help businesses build reliable applications. Our team can help you identify potential vulnerabilities and implement appropriate security measures to strengthen your application’s protection.